

























The Photocopy Problem Is Bigger Than the QR Code
Pakistan’s most dangerous identity technology may still be the office photocopier.
Citizens are asked to submit CNIC copies at residential gates, schools, employers, hotels, mobile shops, hospitals, courier counters and government offices—often without any meaningful explanation of retention, access or destruction. Those copies accumulate in drawers, WhatsApp groups, email inboxes and poorly secured databases. Nobody tells the citizen who will see them, how long they will remain stored or what happens after the original purpose ends.
A QR code could make this worse because it allows bulk capture without manual typing. A clerk who previously saw a photocopy can now extract standardized fields into a database within seconds. The QR does not provide direct access to NADRA’s entire database, but that reassurance misses the immediate privacy question: what information is already embedded inside the QR, and what can the scanning application save?
A photocopied QR is not necessarily a forged credential. It may be something more subtle—a replay of an authentic credential. If the scanner checks only NADRA’s signature, it may correctly report that the data was once issued by NADRA. That does not prove the person presenting the image is the citizen, that the citizen consented to the scan, or that the card remains active today. NIST explicitly notes that digital signatures do not inherently provide replay protection.
This is the same governance dilemma raised by Pakistan’s RoadDex surveillance debate: a useful verification technology becomes dangerous when access, retention, accountability and anti-abuse controls are treated as optional paperwork.
A Cancelled Card Must Not Remain “Valid” Forever
The most important unanswered technical question is not whether the code scans. It is what the verifier does after scanning it.
An offline signature can establish that NADRA issued a particular payload and that it has not been modified. It cannot, by itself, know that NADRA blocked the CNIC yesterday because the card was lost, cancelled, surrendered, replaced or placed under further verification. A static QR remains static.
A high-assurance verifier should therefore check the credential’s current status against NADRA’s systems or a recently synchronized, privacy-preserving revocation list. The W3C Bitstring Status List specification demonstrates how digital credentials can publish suspension and revocation information efficiently without exposing an entire personal record during every status check.
NADRA must explain whether PakID performs a live status query, whether authorized institutional software can work offline, how old cached revocation information may be, what the application displays during a network failure, and whether a successful scan means “signature valid,” “card currently active,” or “identity and live bearer both verified.” Those are radically different assurances, and collapsing them behind a green checkmark would be irresponsible.
Aadhaar Is Useful Evidence—but It Is Not Proof of NADRA’s Implementation
India’s Aadhaar ecosystem demonstrates that digitally signed QR credentials can function at enormous scale. UIDAI’s official Secure QR Code specification describes demographic information, a compressed photograph, hashed contact details and a digital signature that can be verified using a public key.
That comparison supports NADRA’s architectural direction, but Pakistan should not lazily claim it is running “the exact same model.” A secure identity system is defined by its payload, cryptographic algorithms, key rotation, application security, verifier permissions, revocation method, retention rules and redress mechanisms—not merely by the presence of a QR square.
Aadhaar shows that the concept is tested. It does not relieve NADRA of publishing its own specification.
Why Not NFC?
The public demand for NFC is understandable but occasionally oversimplified. NFC is not automatically secure merely because a phone can tap it, just as QR is not automatically insecure because a camera can photograph it. Security depends on whether the NFC implementation uses a passive data tag, a secure element, protected access protocols or cryptographic challenge-response.
A hybrid QR-plus-NFC card could be an excellent future model. QR would support universal, low-cost verification, while a secure NFC component could enable higher-assurance use cases, holder-controlled access and cryptographic operations. It would also preserve a path toward stronger international interoperability.
However, putting NFC on a CNIC would not automatically give it “global recognition.” Pakistan’s e-passport operates within the internationally standardized machine-readable travel-document ecosystem documented in ICAO Doc 9303. A national ID requires its own trust relationships and acceptance agreements. Global recognition comes from standards, certification and verifier trust—not from attaching an antenna to plastic.
NADRA could nevertheless pilot NFC for NICOP, diplomatic, high-assurance government or professional-credential applications while maintaining QR for mass deployment. That would be a smarter engineering debate than pretending Pakistan must select one technology for every identity transaction.
The Design Criticism Is Valid
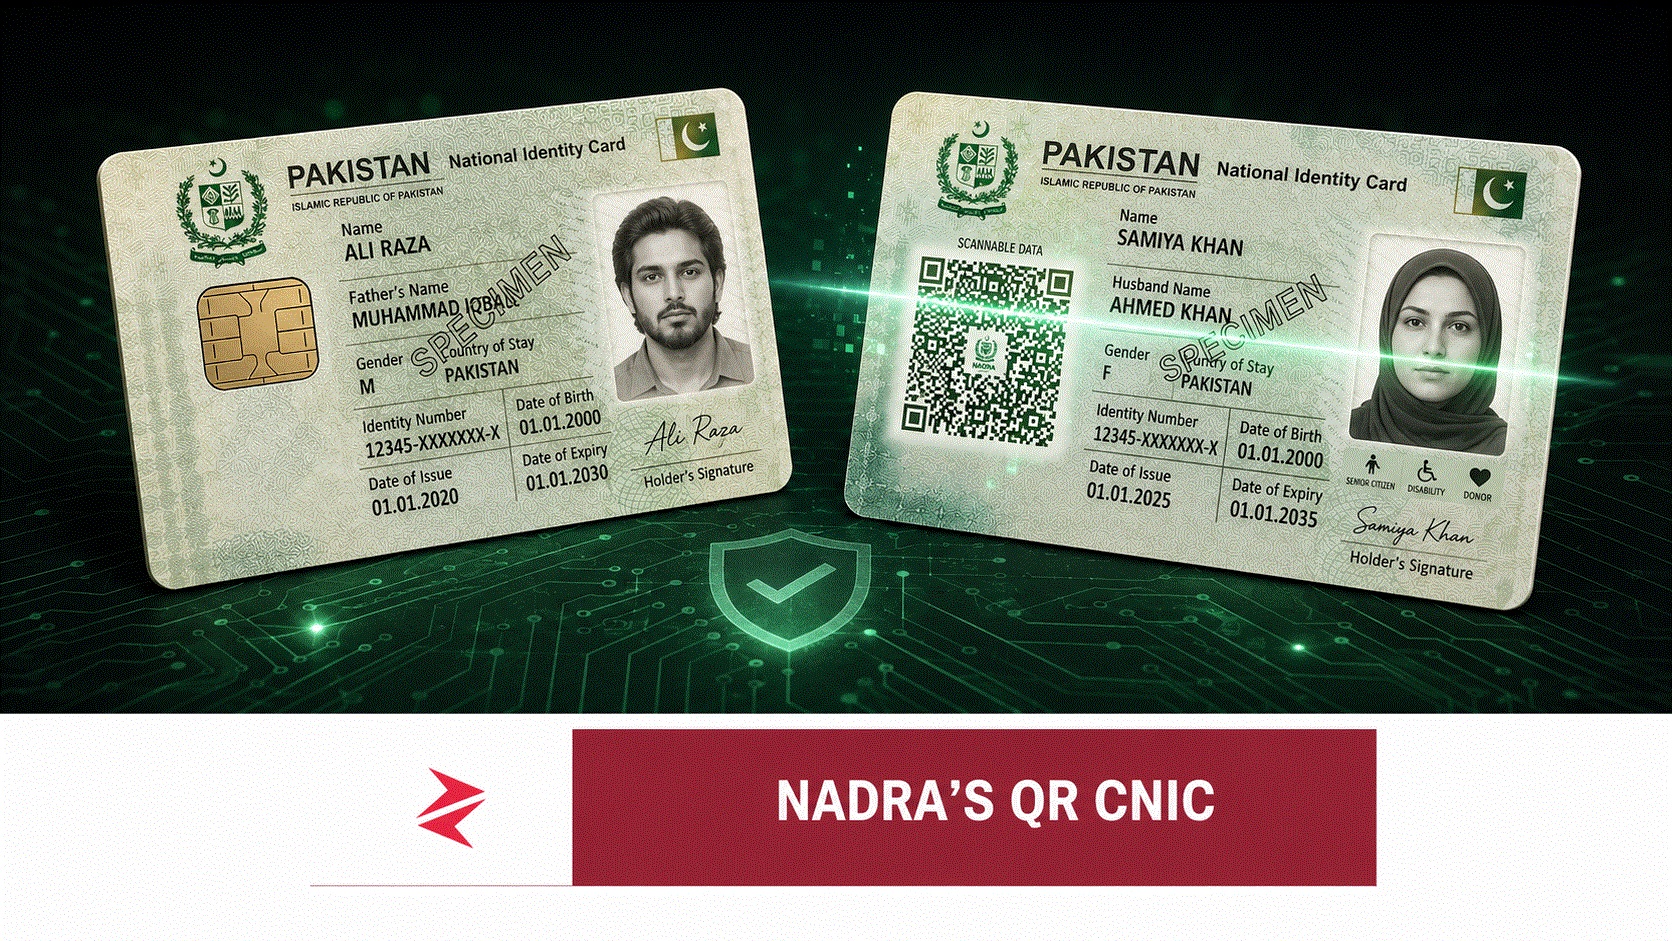
The new card looks like an identity document designed around what the scanner wants to see rather than what a Pakistani citizen wants to carry.
The QR area dominates the front, competes with the portrait and compresses the human-readable hierarchy. The specimens also suggest a second large machine-readable block on the reverse. The result resembles a shipping or inventory label more than a refined national identity document. Public criticism that the QR should be smaller or placed on the back is not superficial vanity. A CNIC is a representation of the state, and visual dignity matters.
The card does deserve credit for its laser-etched photograph, updated UV markers, local polycarbonate construction and Pakistani security-printing capability. Manufacturing identity documents through NSPC is a genuine step toward national self-reliance. Pakistan should expand local expertise in security documents instead of remaining permanently dependent on imported vendors.
Yet patriotic manufacturing does not require citizens to pretend the layout is attractive. NADRA should commission independent security and usability testing, invite Pakistani identity-document specialists and graphic designers into a controlled redesign process, and test how the QR performs after years of scratches, fading, lamination damage and repeated photocopying. A secure code that becomes unreadable under ordinary Pakistani usage conditions is not secure in practice.
What NADRA Must Publish Before Declaring Victory
NADRA should release a non-sensitive technical white paper identifying the QR data fields, signature algorithm, trust-chain model, key-rotation process, verifier authorization tiers, offline behaviour, revocation logic, scan logging, retention limits and response to damaged or copied codes. Publishing this information would not hand criminals a master key; serious cryptography is expected to remain secure even when its architecture is understood.
It should also prohibit routine retention of complete QR payloads where a simple “verified” response is sufficient, provide citizens with a history of institutional verification events, introduce penalties for unauthorized scanning or storage, and finally begin dismantling Pakistan’s photocopy culture.
For banks, hospitals, telecom operators and KYC vendors, the message is equally direct: do not treat a successful QR scan as permission to warehouse every returned field. Organizations preparing integrations should commission an independent privacy-by-design and identity-workflow review before deployment. Enterprises needing that assessment can initiate a technology and operational-risk inquiry through Zorays Khalid.
Frequently Asked Questions
Is NADRA’s QR CNIC an upgrade or a downgrade?
It is an operational and manufacturing upgrade because it replaces an underused imported chip with locally produced, smartphone-accessible verification. Its privacy and high-assurance security remain unproven until NADRA publishes the QR and verifier specifications.